Apply MITRE ATT&CK Framework to Identify Attacker Techniques

Business Scenario
Welcome!
You are a Junior SOC Analyst at CyberSecure Solutions. The SOC has detected several suspicious activities on a test workstation.
Your task is to analyze the available security events, identify what the attacker is trying to achieve, and map the observed activities to the MITRE ATT&CK framework.
Pre-Lab Preparation
Topic : Incident Response and Investigation
1) Introduction to SIEM tools such as Splunk and Wazuh
2) Alert triaging and investigation process
3) Threat detection techniques
Task 1: Understand MITRE ATT&CK
Understand how MITRE ATT&CK describes attacker behavior.
1
Steps
a
-
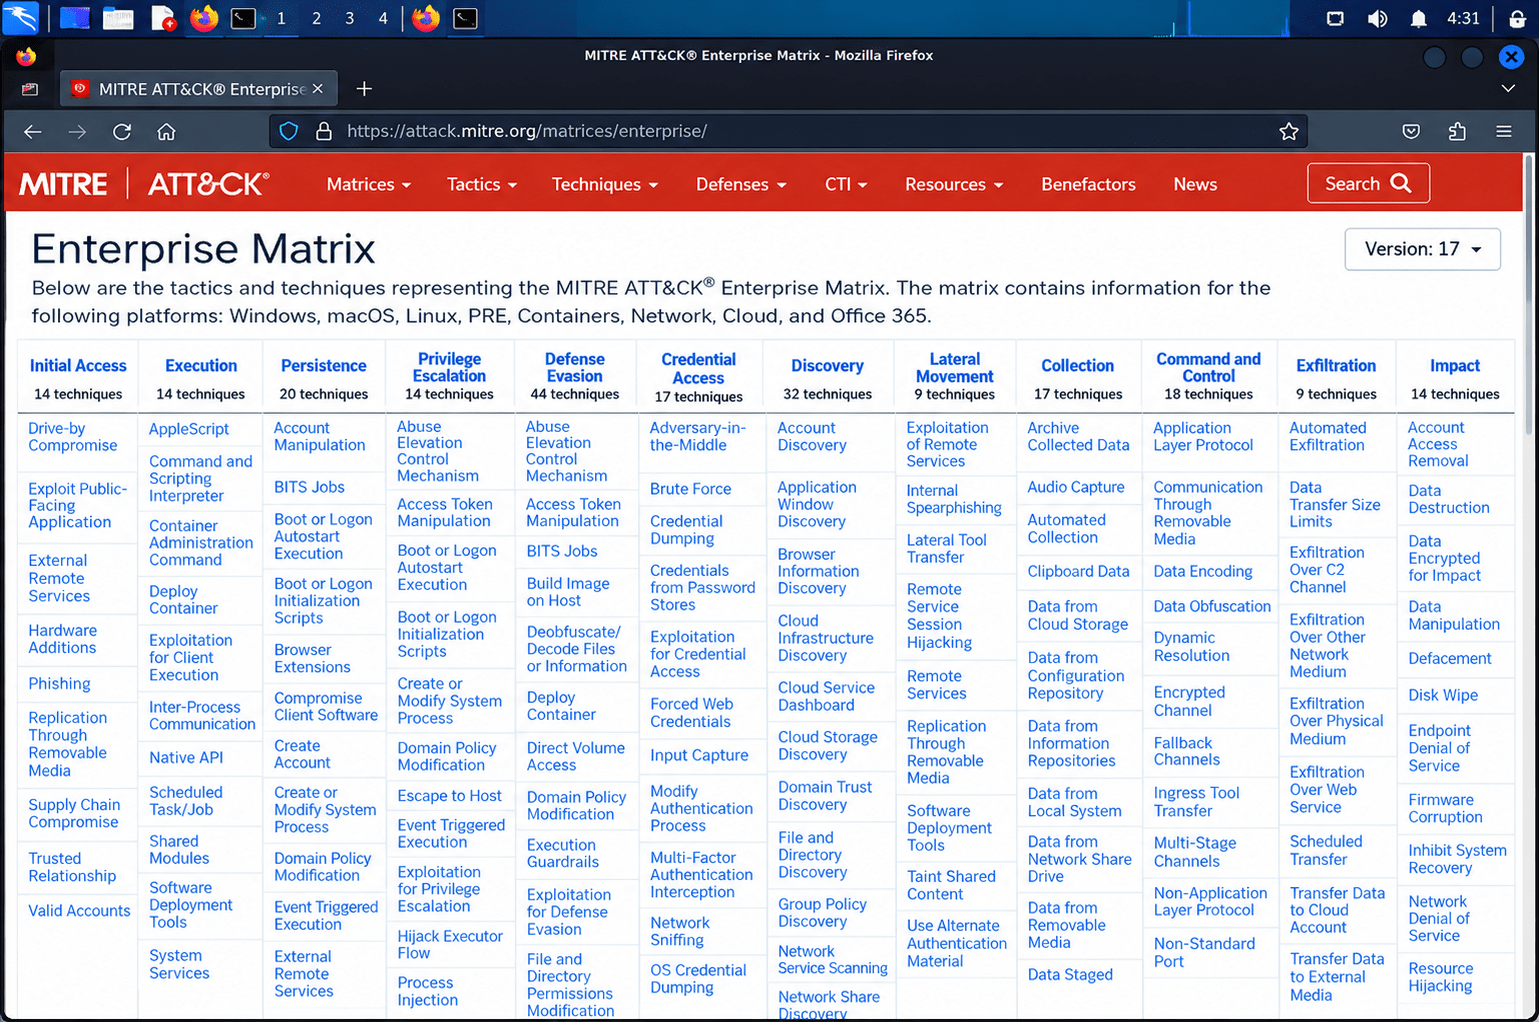
Open the MITRE ATT&CK framework.
-
Review the main Tactics.
-
Select a few common techniques.
-
Understand the difference between:
-
Tactic → Why the attacker is doing something.
-
Technique → How the attacker performs it.
-
-
Open the MITRE ATT&CK framework.
-
Review the main Tactics.
-
Select a few common techniques.
-
Understand the difference between:
-
Tactic → Why the attacker is doing something.
-
Technique → How the attacker performs it.
-
Task 2: Analyze Security Events
Identify attacker behavior from security logs.
1
Steps
a
-
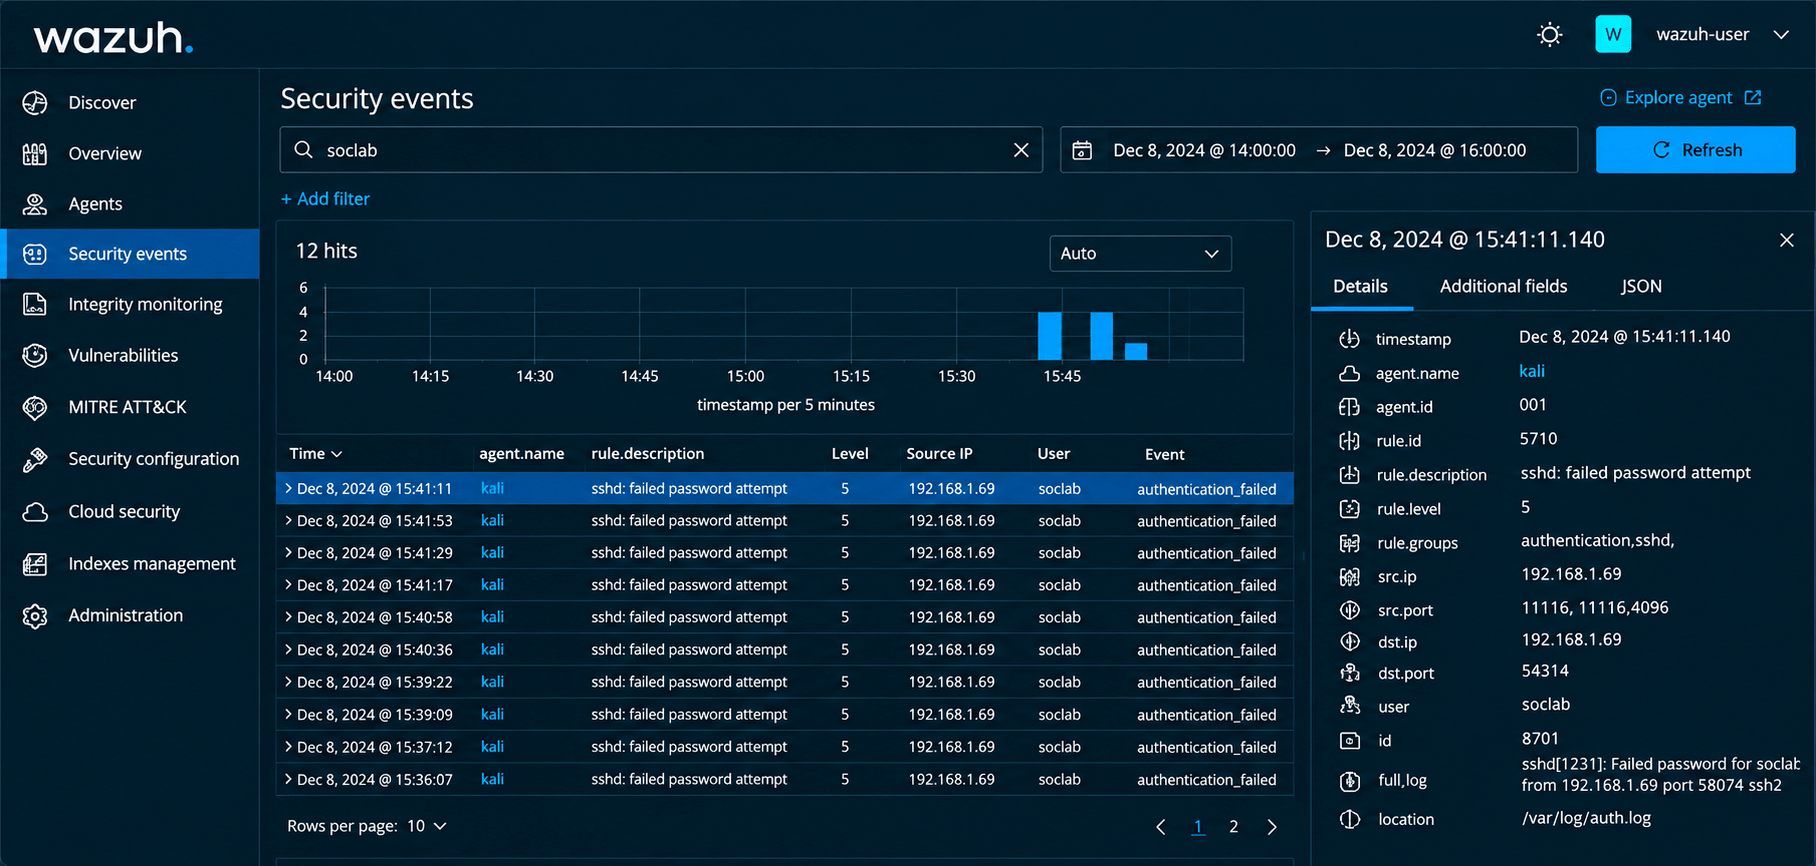
Open the SIEM dashboard.
-
Review the provided security events.
-
Identify suspicious activities.
-
Record:
-
Timestamp
-
Source
-
User
-
Activity
-
Affected system
-
-
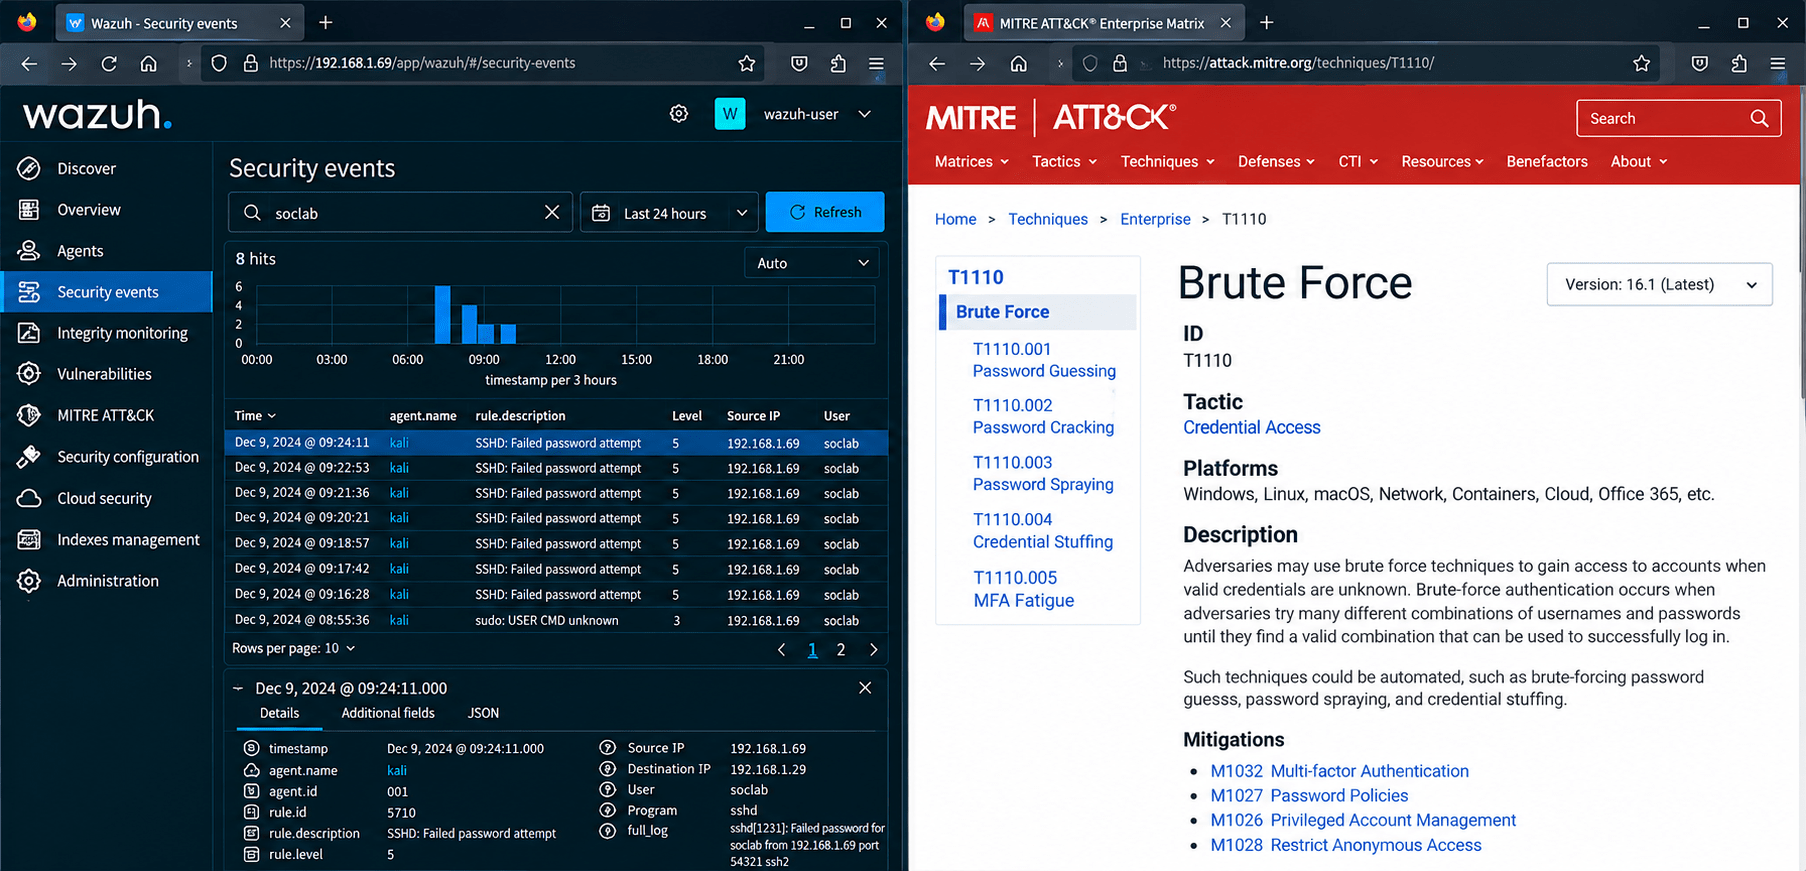
Determine what the activity may represent.
Task 3: Map Activities to MITRE ATT&CK
Map observed behavior to the appropriate MITRE ATT&CK technique.
1
Steps
a
-
Select a suspicious activity.
-
Search for the activity in MITRE ATT&CK.
-
Identify the matching technique.
-
Record:
-
Tactic
-
Technique
-
Technique ID
-
Evidence
-
-
Repeat for the remaining events.
Task 4: Build an Attack Chain
Understand how multiple techniques can form an attack sequence.
1
Steps
a
-
Arrange the identified techniques in chronological order.
-
Identify the tactic associated with each technique.
-
Create an attack-chain diagram.
Task 5: Document the Findings
Create a simple MITRE ATT&CK-based security report.
1
| Field | Example |
|---|---|
| Finding ID | ATTACK-001 |
| Observed Activity | PowerShell Execution |
| Tactic | Execution |
| Technique | PowerShell |
| Technique ID | T1059.001 |
| Evidence | SIEM Log |
| Severity | Medium |
| Recommendation | Monitor PowerShell activity |
Click to view : SOC incident report
Great job!
You have successfully completed your MITRE ATT&CK Technique Identification lab.
In this lab, you have: Understood the MITRE ATT&CK Framework, Mapped attacker behaviors to techniques, Identified relevant attack techniques, Analyzed attacker activities
You are now ready to move to the next stage of threat analysis and detection.
Checkpoint
Great job!
You have successfully completed your MITRE ATT&CK Technique Identification lab.
In this lab, you have: Understood the MITRE ATT&CK Framework, Mapped attacker behaviors to techniques, Identified relevant attack techniques, Analyzed attacker activities
You are now ready to move to the next stage of threat analysis and detection.
Checkpoint
Next-Lab Preparation
Topic : Incident Response and Investigation
1) Introduction to SIEM tools such as Splunk and Wazuh
2) Alert triaging and investigation process
3) Threat detection techniques